AI workflow automation security
AI Workflow Automation Security: What Small Businesses Should Not Ignore
AI automation security is not only about picking a trusted tool. For a small business, the bigger question is what the workflow can read, what it can change, who approves risky actions, and what happens when something looks wrong.
Security is a workflow decision, not only an IT decision
Most small business owners do not wake up thinking about AI security. They think about late follow-ups, manual reporting, customer replies, invoice checks, and internal questions that keep interrupting the team.
That is understandable. The business problem comes first. But the moment AI automation touches a real workflow, security becomes part of the business process. Not later. Not after the pilot. Before the first customer record, invoice, email thread, or proposal template is connected.
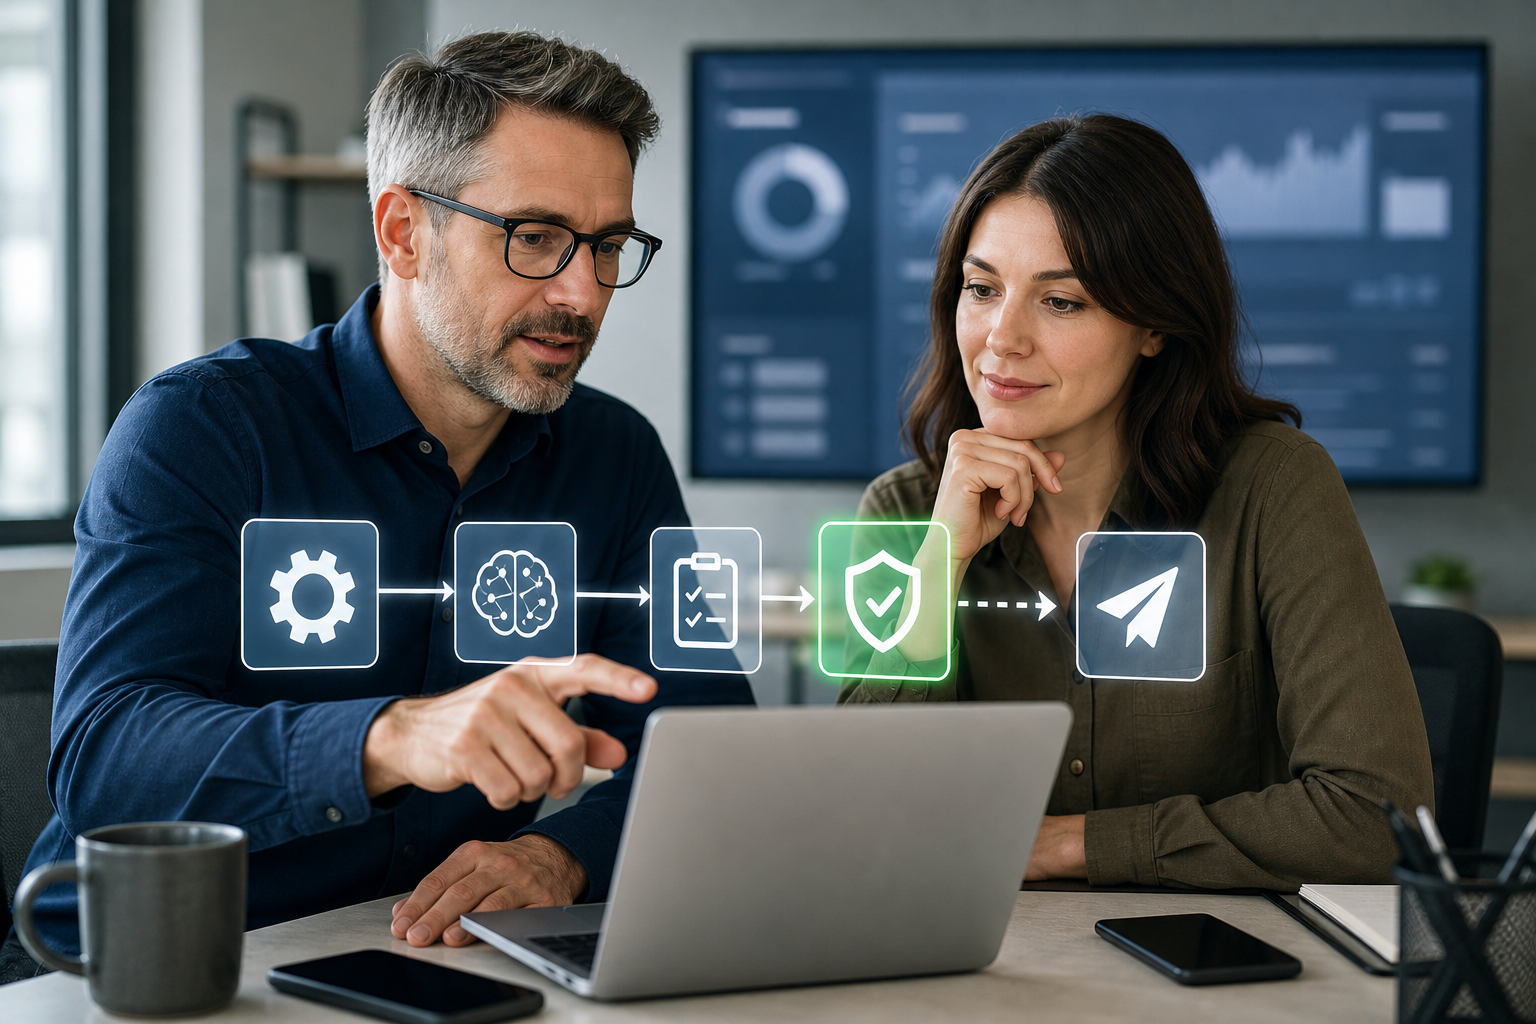
The practical issue is simple: AI workflows often sit between systems. A workflow might read a form, pull CRM context, draft an email, summarize a document, update a task, and alert a manager. Each step can be useful. Each step also creates a security question.
Who can see the data? Which system is the source of truth? Can the automation send messages externally? Can it write back to the CRM? Are prompts and outputs logged? What happens if a customer shares private information in a form? What happens if the AI is confidently wrong?
This is why the pillar guide on working with an AI automation consultant for small business starts with leverage and workflow clarity. A useful automation is not just a clever connection between tools. It is a business process with controls.
Good AI automation security is usually boring: smaller access, clearer approvals, better records, vendor checks, and a habit of testing before expanding.
For SMBs, that is good news. You do not need enterprise theater for the first pilot. You need a few practical decisions made before the workflow is allowed to act on behalf of the business.
The seven security checks before AI workflow automation
If you are considering AI workflow automation, use these seven checks before connecting the workflow to real business systems. They are written for owners and operators, not security departments.
1. Decide what the workflow is allowed to read
Start with the smallest data set that can prove the workflow. If the automation is helping with client intake, it may need the form submission, selected service page content, qualification rules, and a few examples of good follow-up questions. It does not need full inbox access, payroll folders, legal files, or every CRM note from the last ten years.
Access grows quietly. A simple pilot becomes risky when the tool asks for broad permissions because it is easier to set up. The owner should ask: what is the minimum access needed for this workflow to work?
This connects directly to the previous article on data needed before AI automation. Better source selection reduces both errors and security exposure.
2. Decide what the workflow is allowed to change
Reading data is one risk. Changing data is another. A workflow that drafts a reply is safer than one that sends it automatically. A workflow that suggests a CRM update is safer than one that overwrites records. A workflow that flags an invoice is safer than one that approves payment.
For a first pilot, I would usually keep write access narrow or require human approval before anything customer-facing, financial, legal, or operationally sensitive happens. The goal is not to slow everything down. The goal is to prevent a small experiment from becoming a business incident.
3. Check vendor data handling before you upload anything sensitive
Before you put company data into an AI tool, review the vendor's business data terms. Look for training defaults, retention, encryption, admin controls, audit logs, user access, support access, connected apps, and data residency if that matters for your business.
OpenAI states that business and API customer data is not used for model training by default. Microsoft describes Copilot as working within existing Microsoft 365 permissions. Those are useful commitments, but they do not remove your responsibility to configure the workspace properly.
Small business version: do not paste private customer data into personal tools. Do not connect a tool to every file because it is convenient. Do not let each team member create a separate AI setup with no shared rules.
4. Protect against prompt injection and untrusted inputs
Prompt injection sounds technical, but the business version is easy to understand. If an AI workflow reads untrusted content such as emails, web pages, support tickets, uploaded documents, or customer messages, that content may contain instructions that try to manipulate the AI.
For example, an uploaded document could include a hidden instruction telling the AI to ignore company policy or reveal information. A customer email could tell the AI to change routing rules. A scraped web page could try to influence a research workflow.
The answer is not panic. The answer is containment. Treat external content as untrusted, separate instructions from data, limit what the workflow can do, validate outputs before action, and keep sensitive actions behind human approval.
5. Put human review where judgment or trust matters
Some workflows can be mostly automated. Others should stay human-reviewed because they affect trust, money, relationships, or legal exposure. A customer refund, contract change, payroll question, complaint response, security alert, finance approval, or HR matter should not be handed to AI without review.
This is the same point made in the guide to human-in-the-loop AI workflows. Full automation is not always the best business design. Sometimes the smarter workflow is AI-assisted preparation followed by a person making the decision.
6. Keep logs that a business owner can understand
If an automation makes a recommendation, drafts a message, classifies a lead, or updates a record, the business should be able to answer four questions later: what data did it use, what did it produce, who approved it, and what changed?
Logs do not need to be complex in the first pilot. A simple record of input source, AI output, reviewer, decision, timestamp, and exception reason can be enough. The important part is accountability. If something goes wrong, you should not have to guess what happened.
7. Plan how to pause the workflow
Every AI automation should have a stop button. If outputs become strange, permissions are wrong, a vendor setting changes, a customer complains, or the team spots a risk, someone must know how to pause the workflow quickly.
This sounds obvious until a business has several automations running through personal accounts, shared inbox rules, third-party connectors, and old API keys. Write down who owns the workflow, where it runs, what credentials it uses, and how to disable it.
Practical examples small businesses should recognize
Security becomes clearer when you apply it to real workflows. Here are four common examples.
Lead follow-up automation
A lead follow-up workflow may read form submissions, summarize the request, check qualification rules, and draft a reply. The security risk is not only the AI model. It is the intake form, CRM access, email sending permission, and whether the workflow can expose private prospect information to the wrong person.
A safer first version drafts the reply, suggests a lead score, and creates a task for a person. It does not send external emails automatically until the owner has reviewed enough examples.
Invoice and finance checks
An invoice workflow may extract supplier, amount, due date, purchase order match, tax details, and bank information. This can save time, but finance workflows need tight controls. The AI can flag mismatches and prepare a review summary. It should not approve payment or change bank details without human control.
The FTC's business security guidance is useful here because it brings the topic back to basics: collect only what you need, keep it safe, limit access, and make sure service providers meet reasonable security expectations.
Customer support replies
AI can help draft answers to repeated customer questions. The risk appears when the workflow sees private customer history, payment issues, refund requests, complaints, or legal language. The safest first workflow uses approved knowledge sources, drafts replies, and routes sensitive cases to a person.
The broader AI workflow automation principle is simple: automate preparation and routing first, then expand only after the process is stable.
Internal knowledge search
Internal AI search can be useful when the team asks the same questions every week. But it can also reveal overshared files. If everyone has access to old HR notes, private contracts, or sensitive finance folders, an AI assistant may surface that content because existing permissions allow it.
Before launching internal search, clean up access. Decide which folders are approved, archive outdated documents, and restrict sensitive sources. This is not an AI problem. It is a permissions problem that AI makes more visible.
A simple AI automation security scorecard
Use this scorecard before you move an AI workflow from experiment to daily use.
| Security question | Good enough to pilot | Fix before expanding |
|---|---|---|
| Access | The workflow only reads the sources needed for one narrow job. | The tool has broad inbox, drive, CRM, or finance access by default. |
| Actions | AI drafts, flags, classifies, or suggests. A person approves risky actions. | The workflow can send, approve, delete, overwrite, or escalate without review. |
| Vendor review | Training defaults, retention, encryption, admin roles, and connected apps are understood. | Data is uploaded because the tool is convenient, not because the risk was reviewed. |
| Untrusted input | External emails, files, forms, and web content are treated as data, not instructions. | The workflow follows instructions found inside customer messages or uploaded documents. |
| Logging | The business can review input source, output, approver, decision, and exception reason. | Nobody can explain what the automation did after the fact. |
| Pause plan | One owner knows where the workflow runs and how to stop it. | The workflow depends on personal accounts, unclear credentials, or undocumented connectors. |
What should stay human-reviewed
The first AI automation project should not try to prove that people are unnecessary. It should prove that repeated work can be prepared faster, checked better, and handed to the right person at the right time.
Keep human review for customer complaints, legal language, contract changes, payment approval, bank details, HR issues, medical or sensitive personal data, security incidents, high-value sales, and anything that could damage trust if handled poorly.
That still leaves plenty of useful work for AI: summarizing intake forms, drafting first replies, classifying support requests, comparing invoices to purchase orders, preparing weekly reports, extracting action items, searching approved knowledge sources, and flagging exceptions.
If you are unsure where your business stands, start with the AI Readiness Checklist. It gives you a practical first view of whether your workflow, data, and team habits are ready for automation.
How to test safely before going live
A safe AI automation pilot is narrow, measured, and reversible. It uses real examples but avoids broad access. It keeps a person in control. It measures whether the workflow actually improved.
Use this pilot structure:
- Choose one repeated workflow with a clear owner.
- Write down what the automation may read, draft, update, and never touch.
- Use a small set of real examples, with sensitive data removed where possible.
- Review vendor terms before uploading or connecting company data.
- Keep customer-facing, financial, legal, and HR actions under human approval.
- Log outputs, approvals, corrections, and exceptions during the pilot.
- Test prompt injection and bad-input cases with example emails, files, and forms.
- Document how to pause, disable, or roll back the workflow.
At the end of the pilot, do not only ask whether the AI worked. Ask whether the business trusts the workflow. Did it reduce time? Did it catch errors? Did it create new risks? Did people understand when to override it? Did it stay inside the agreed boundaries?
If the answer is not clear, keep the workflow smaller. AI automation should earn more access by performing well under review.
The Full AI Business Assessment is designed for exactly this kind of decision. It reviews the workflow, business value, data, risk, tool fit, approval points, and realistic next step before you invest in a larger build. If you are earlier, take the free AI assessment and identify which workflow deserves attention first.
Make the first AI workflow useful and controlled
If your business is considering AI automation, do not start by connecting every system. Start with one repeated workflow, one clear business outcome, and the smallest secure pilot that can prove value.
Sources reviewed
I reviewed these sources on August 17, 2026 while preparing this guide, focusing on AI risk management, prompt-injection risk, vendor controls, permissions, and practical security habits for SMB workflows.
- NIST: AI Risk Management FrameworkReviewed for governance, mapping, measuring, and managing AI risks across the AI system lifecycle.
- NIST: Generative AI Profile for the AI RMFReviewed for generative AI risk categories and practical risk-management guidance.
- OWASP: Top 10 for LLMs and GenAI ApplicationsReviewed for prompt injection, sensitive information disclosure, excessive agency, overreliance, and related LLM application risks.
- CISA and UK NCSC: Guidelines for Secure AI System DevelopmentReviewed for secure-by-design guidance covering AI system design, development, deployment, and operation.
- Microsoft Learn: Security for Microsoft 365 CopilotReviewed for existing-permission behavior, oversharing risk, enterprise data protection, and governed data foundations.
- OpenAI: Business data privacy, security, and complianceReviewed for business data training defaults, encryption, retention controls, access management, audit logs, and compliance features.
FAQ
What is AI automation security for a small business?
AI automation security means controlling what an AI workflow can read, suggest, update, send, and store. For a small business, it usually includes permission limits, vendor checks, human approval, logging, prompt-injection protection, and a clear way to pause the workflow.
Should small businesses avoid connecting AI to customer data?
Not always. Customer data can be used safely when the workflow has a clear purpose, minimal access, approved vendor terms, privacy controls, and human review for sensitive actions. The first pilot should use the smallest data set that can prove the business value.
What AI workflow actions should require human approval?
Human approval should be required for customer-facing messages, payment or finance decisions, legal or contract language, HR matters, sensitive customer information, complaints, security incidents, and high-value decisions. AI can prepare the work, but a person should own the judgment.
How can an SMB test AI automation security before launch?
Test one narrow workflow with limited access, real examples, human review, logging, bad-input cases, and a pause plan. Track corrections, overrides, exceptions, and business results before giving the workflow more access or autonomy.
